

 Unified Zero Trust CNAPP


 Secure APIs
 Secure Kubernetes
 SIEM
 Secure Secrets


10 Best API Security Tools in 2026: From Discovery to Runtime Protection

Modern APIs are everywhere, but most organizations still rely on incomplete tools that only cover a slice of the attack surface. This guide reviews the 10 best API security tools in 2026 and groups them across discovery, testing, and runtime protection so cloud-native teams can design an end-to-end defense strategy.
Reading Time: 15 minutes


Table of Contents


TL;DR
- APIs are a major attack surface in modern applications; attacks exploit valid credentials, excessive permissions, and business logic flaws.
- Effective API security requires end-to-end coverage: discovery, shift-left testing, and runtime protection.
- Perimeter tools like gateways and WAFs alone are insufficient, especially for internal and east–west APIs.
- Runtime API security, as offered by platforms like AccuKnox, detects anomalies and enforces zero-trust policies inside Kubernetes and cloud-native environments.
- Choosing tools with CI/CD integration, zero-trust support, runtime coverage, and scalable pricing ensures protection keeps pace with rapid API deployments.
The best API security tools in 2026 help teams secure the full API lifecycle: discovery, testing, posture management, and runtime protection. Tools like Salt Security and Imperva are strong for discovery and traffic analysis, 42Crunch, Postman, and Burp Suite support design-time and testing workflows, while AccuKnox stands out for runtime API security, zero-trust enforcement, and Kubernetes-native protection for internal and east-west APIs.
APIs are a major attack surface in modern applications; attacks exploit valid credentials, excessive permissions, and business logic flaws. Effective API security requires end-to-end coverage: discovery, shift-left testing, and runtime protection. Perimeter tools like gateways and WAFs alone are insufficient, especially for internal and east-west APIs. Runtime API security, as offered by platforms like AccuKnox, detects anomalies and enforces zero-trust policies inside Kubernetes and cloud-native environments. Choosing tools with CI/CD integration, zero-trust support, runtime coverage, and scalable pricing ensures protection keeps pace with rapid API deployments.
APIs now power everything from mobile apps to AI workflows, yet they remain one of the most exploited attack surfaces. According to the OWASP API Security Top 10, API-related attacks continue to rise each year. Reports from Gartner show that API attacks are a major concern for security leaders. Industry reports consistently show APIs accounting for a majority of modern application traffic and a growing share of breaches. Choosing the right API security tools is no longer about point solutions; it’s about building coverage across discovery, testing, and runtime protection. This blog reviews the 10 best API security tools in 2026 to help security and platform teams design an end-to-end, cloud-native defense.
Essential API Security Features to Look for in 2026

Modern API environments are dynamic, distributed, and heavily automated. The tools you choose must go beyond basic gateway controls or occasional scans.

| Feature | What It Does | Benefit vs Pain Point | Example Outcome If Missing |
|---|---|---|---|
| Continuous API Discovery & Inventory | Automatically identifies all APIs documented, undocumented, shadow, and zombie by observing traffic and configurations | Security teams often protect only known APIs; discovery eliminates blind spots caused by rapid releases and third-party integrations | A deprecated internal API still accessible externally is flagged before exploitation |
| Shift-Left API Security Testing | Tests APIs during design and CI/CD stages for OWASP API Top 10 risks | Fixing vulnerabilities in production is costly and disruptive | Detecting broken object level authorization (BOLA) in an OpenAPI spec before release |
| Runtime Behavior Monitoring | Observes live API traffic to establish normal behavior patterns | Many API attacks appear legitimate at the surface | Identifying abnormal request sequences that signal business logic abuse |
| Policy-Driven Enforcement (Zero Trust) | Enforces least-privilege access and behavior-based policies at runtime | Static rules don’t adapt to dynamic microservices environments | Blocking an API call that violates workload-level communication policies in Kubernetes |
| Cloud-Native & Kubernetes Awareness | Integrates natively with containers, service meshes, and orchestration layers | Traditional perimeter tools lack internal visibility | Securing internal service-to-service APIs inside Kubernetes |
Understanding the API Visibility Gap
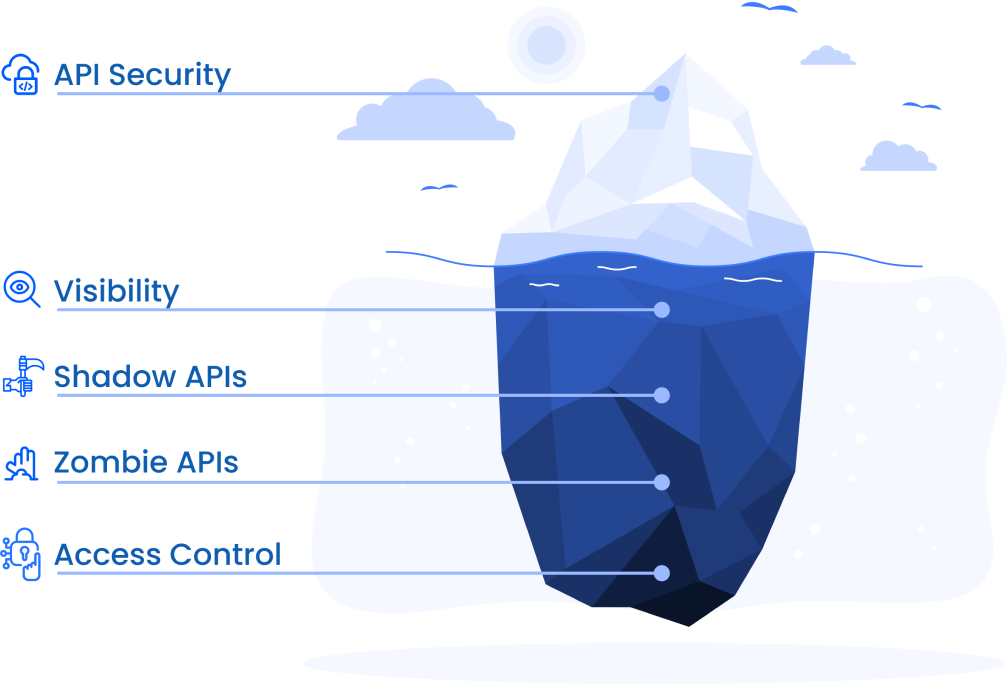
You can’t secure what you can’t see. Most enterprises discover they have 40–60% more APIs than their gateway configurations show — shadow APIs, zombie endpoints, and untracked microservice connections. Gateways only see traffic explicitly routed through them; internal microservice calls, pod-to-pod traffic, and Kubernetes sidecar communication never touch a gateway. Three architectural shifts compound the gap: the microservices explosion (hundreds of internal service-to-service endpoints that never touch a gateway), Kubernetes ephemerality (pods that live minutes and vanish from static inventory), and the AI API layer (calls to model endpoints, vector databases, and MCP servers determined by runtime inference, not any static spec).
| Gap Type | Root Cause |
|---|---|
| Gateway Blind Spots | APIs that receive traffic but were never registered with any gateway — microservice-to-microservice calls, internal platform APIs, debug endpoints deployed outside CI/CD. |
| Sampling Gaps | Traffic-analysis tools capture only 1–10% of calls; low-frequency, high-value calls (admin endpoints, privilege-escalation paths) run in the unsampled window. |
| Agent Gaps | Agent-based tools require per-host/pod installation; in dynamic Kubernetes environments, pods spin up faster than agents deploy. |
| Drift Gaps | Code scanning produces an accurate inventory at deployment and nothing after — APIs change at runtime as parameters and auth requirements shift. |
| LLM API Connection Gaps | AI applications generate calls to model endpoints, vector databases, and MCP servers at inference time — invisible to any discovery method at the code or gateway layer. |
Four discovery methods exist, and only one closes every gap: gateway inspection sees managed, registered routes only; code/spec scanning gives a baseline inventory that goes stale the moment something changes at runtime; sampled traffic analysis catches high-frequency calls but misses low-frequency, high-value ones; eBPF runtime discovery operates at the kernel level, capturing 100% of API calls both internal and external, across every gap type even without code change. Score any platform on five points before you commit: kernel-level observability, a zero-sampling guarantee, east-west completeness, continuous drift detection, and LLM/AI connection mapping. A platform scoring below 4 of 5 has structural blind spots, not feature gaps.
API Security Tools Comparison Table
| Product | Best For | Deployment Focus | Key Strength | Free Trial |
|---|---|---|---|---|
| AccuKnox | Runtime API security in cloud-native environments | Kubernetes, containers, cloud-native apps | Zero-trust enforcement and runtime visibility for east-west APIs | Yes |
| Salt Security | API discovery and behavioral analysis | Enterprise API estates | Shadow API discovery and anomaly detection | No |
| Akamai API Security | Public-facing API protection at scale | Edge and internet-facing APIs | Bot mitigation and edge protection | No |
| Imperva API Security | API protection with app security integration | Hybrid and public-facing apps | API discovery, OWASP coverage, bot defense | No |
| Cequence Security | Fraud and abuse prevention | External API ecosystems | Abuse detection and business logic attack defense | No |
| 42Crunch | Shift-left API security testing | DevSecOps and CI/CD | OpenAPI testing, governance, and scanning | Limited |
| Postman | API collaboration and testing | Developer and QA workflows | Automated API testing and collections | Yes |
| Burp Suite | Manual and advanced API testing | Security testing teams | Deep API pentesting and scanning | Yes |
| Apigee | API management with security controls | Enterprise API programs | Gateway, auth, quota, and analytics | No |
| Kong | API gateway extensibility | Cloud, hybrid, and microservices | Flexible gateway and plugin ecosystem | Yes |
Top API Security Tools in 2026
1. AccuKnox

What It Is
AccuKnox is a cloud-native API runtime security platform purpose-built for modern microservices and Kubernetes environments. Unlike perimeter or gateway-based tools that inspect API traffic at the edge, AccuKnox secures APIs where they actually execute inside the cluster by combining runtime visibility, behavioral analysis, and zero-trust enforcement. This approach is particularly effective against API attacks that exploit valid credentials, excessive permissions, or complex business logic.
AccuKnox continuously observes API calls between services, users, and workloads to build a baseline of normal behavior. Any deviation such as unusual request patterns, unexpected API access paths, or privilege escalation attempts is detected in real time and can be blocked using fine-grained policies. This makes AccuKnox well-suited for protecting internal, east-west APIs that are invisible to traditional WAFs and gateways.
Key API Security Capabilities:
- Runtime API behavior monitoring that detects abnormal request sequences, data access patterns, and business logic abuse
- Kubernetes-native API enforcement using identity-aware and workload-aware policies, without code changes
- Zero-trust API access controls that enforce least privilege for service-to-service and user-to-service calls
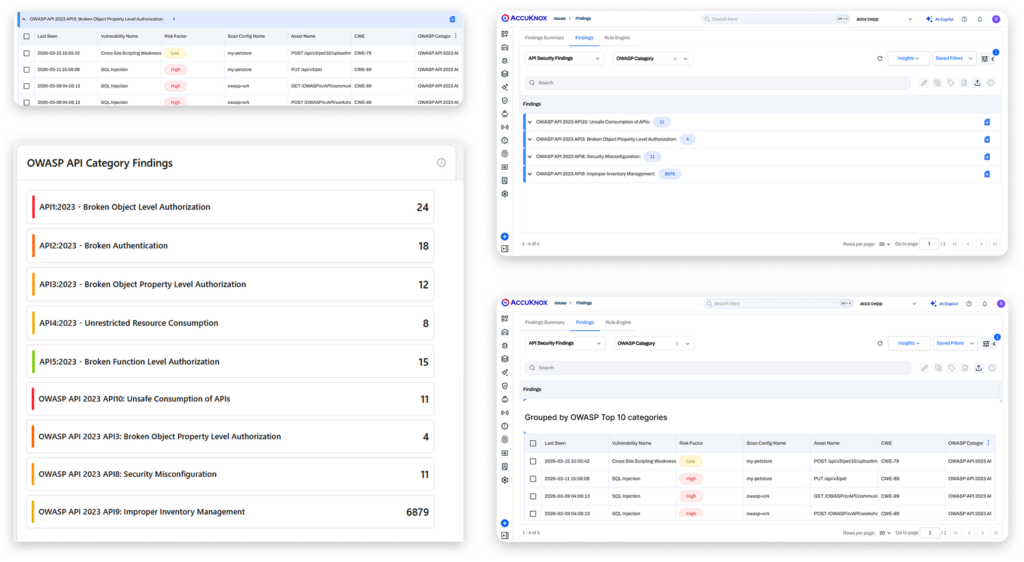
- Protection against OWASP API Top 10 risks, including BOLA, excessive data exposure, and mass assignment, at runtime
- API inventory and exposure assessment derived from live traffic, helping teams understand which APIs are actually used
- Policy-as-code support that allows security teams to version, audit, and automate API security controls
- Real-time visibility for newly deployed APIs, ensuring security keeps pace with rapid CI/CD releases

AccuKnox Provides Visibility on OWASP Top 10 Findings for API Security
Who It’s Best For:
AccuKnox is ideal for platform engineering, DevSecOps, and security teams running Kubernetes-based or cloud-native applications where APIs form the backbone of internal and external communication.
Pros:
- Deep, execution-level visibility into API behavior
- Strong coverage for internal and east-west APIs
- Enforces security without impacting developer velocity
Cons:
- Requires Kubernetes or containerized workloads to unlock full value
2. Salt Security

What It Is
Salt Security is a dedicated API security platform focused on continuous API discovery and behavioral analysis. It inspects live API traffic to identify undocumented, shadow, and zombie APIs while detecting abuse patterns tied to business logic attacks.
Key Features
- Continuous API discovery
- Behavioral anomaly detection
- OWASP API Top 10 mapping
Pros
- Strong visibility into large and complex API estates
- Mature behavioral analytics
Cons
- Limited workload and Kubernetes-level context
3. Akamai API Security

What It Is
Akamai API Security extends Akamai’s edge platform to protect internet-facing APIs from volumetric attacks, bots, and credential abuse using global traffic visibility.
Key Features
- Edge-based API discovery
- Bot and abuse mitigation
- Integration with Akamai WAF
Pros
- Scales effectively for high-traffic public APIs
- Strong DDoS and bot protection
Cons
- Limited visibility into internal service-to-service APIs
4. Imperva API Security

What It Is
Imperva API Security is part of Imperva’s application security portfolio, designed to protect APIs from exploits, automated abuse, and data exposure. It combines API discovery with runtime protection using traffic inspection and threat intelligence.
Key Features
- API discovery and inventory
- OWASP API Top 10 protection
- Bot and automated attack mitigation
Pros
- Strong threat intelligence and research backing
- Works well with Imperva WAF deployments
Cons
- Primarily perimeter-focused
- Limited deep runtime visibility for internal APIs
5. Cequence Security

What It Is
Cequence Security focuses on protecting APIs from business logic abuse, fraud, and automated attacks, particularly in regulated and high-risk industries.
Key Features
- API abuse detection
- Bot and fraud prevention
- Behavioral risk analysis
Pros
- Strong protection against account takeover and fraud
- Proven in regulated sectors
Cons
- Narrower scope beyond abuse prevention
6. 42Crunch

What It Is
42Crunch is an API security testing and governance platform designed for shift-left security using OpenAPI specifications and CI/CD integrations.
Key Features
- Static analysis of API definitions
- CI/CD security checks
- API governance policies
Pros
- Strong design-time security capabilities
- Developer-friendly workflows
Cons
- No runtime threat enforcement
7. Postman

What It Is
Postman is a widely used API development and testing platform that includes security-focused testing for authentication, authorization, and token handling.
Key Features
- API test automation
- Auth and token validation
- CI/CD integrations
Pros
- Easy to adopt for developers
- Large ecosystem
Cons
- Not a dedicated API security platform
8. Burp Suite

What It Is
Burp Suite is a penetration testing toolkit used by security professionals to manually and automatically test APIs for vulnerabilities.
Key Features
- API fuzzing and scanning
- Manual request manipulation
- Vulnerability validation
Pros
- Deep testing flexibility
- Industry-standard for pentesting
Cons
- Requires skilled testers
- Not designed for continuous monitoring
9. Apigee

What It Is
Apigee is an API management platform that provides traffic management, authentication, and analytics as part of a managed API program.
Key Features
- Authentication and authorization
- Rate limiting and quotas
- API analytics
Pros
- Strong management and governance features
- Suitable for mature API programs
Cons
- Limited runtime threat detection
10. Kong

What It Is
Kong is a cloud-native API gateway that manages and secures API traffic using plugins and policy extensions.
Key Features
- Gateway-level authentication
- Rate limiting
- Kubernetes-friendly deployment
Pros
- Flexible and open-core
- Strong Kubernetes support
Cons
- Requires add-ons for advanced security use cases

Important Things to Consider When Choosing an API Security Tool
CI/CD and Kubernetes Integration
APIs are created and updated continuously. Security tools must integrate with CI/CD pipelines and Kubernetes environments to automatically discover and protect newly deployed APIs. Without this, APIs remain exposed between release and remediation.
Zero-Trust Enforcement
Effective API security assumes no request is trusted by default. Tools should enforce least-privilege access based on identity, workload context, and behavior—especially for internal and east–west APIs.
Pricing Transparency and Scalability
API traffic scales rapidly. Look for predictable pricing models that grow with API usage, without hidden costs or penalties that discourage adoption.
Runtime vs Perimeter Coverage
Perimeter tools protect APIs at the edge, but most attacks exploit business logic during execution. Runtime visibility is essential to detect and stop these attacks where they actually occur.
A Weighted Evaluation Checklist for Buyers
Ten criteria for scoring shortlisted vendors, condensed from a dedicated buyer checklist — use it as a scoring sheet across finalists:
| Evaluation Area | Weight | What to Ask Vendors |
|---|---|---|
| Full API discovery & visibility | 15% | How do you discover APIs that never pass through a gateway? Can you monitor east-west traffic in Kubernetes? |
| Behavioral analysis & abuse detection | 15% | Do you baseline normal behavior, or rely mainly on signatures? Can you detect logic abuse and misuse of valid credentials? |
| Kubernetes & microservices fit | 15% | Is the platform built for Kubernetes or adapted to it? Can it observe service-to-service traffic inside clusters? |
| Real-time policy enforcement | 15% | Can the platform take preventive action, or is it alert-only? What controls can be applied progressively in monitor-first mode? |
| No-code-change deployment | 10% | Can protection be deployed without changing application code or adding SDKs? |
| Beyond-WAF detection depth | 10% | What threats can you detect that a WAF cannot? Do you cover OWASP API Top 10 risks at runtime? |
| Real-time response & integrations | 10% | What is the average delay from detection to alert? Which SIEM/SOAR/observability tools are supported? |
| Ownership & business context mapping | 5% | How do you map APIs to owners, environments, and business criticality automatically? |
| Governance & compliance support | 5% | What audit trails, RBAC, and multi-tenant controls exist for large organizations? |
Discovery only works for gateway-managed APIs; internal/east-west traffic isn’t visible; detection is mostly signature-based; policy enforcement is limited or unavailable; deployment requires significant code changes; Kubernetes support feels bolted on; ownership mapping is highly manual; alert volume is high but content is weak; pricing scales poorly with API usage.
API Security vs API Management: What’s the Difference?
API management tools such as gateways and lifecycle platforms help teams publish, route, authenticate, and monitor APIs. They are essential for reliability and access control, but they do not provide full protection against business logic abuse, privilege misuse, shadow APIs, or internal east-west API threats.
API security tools go further by adding:
- Continuous API discovery across documented and undocumented endpoints
- Shift-left testing for OWASP API risks
- Behavioral analytics to detect abuse patterns
- Runtime protection for service-to-service and user-to-service interactions
- Policy enforcement aligned to zero-trust principles
In practice, most organizations need both: API management for control and operability, and API security for risk reduction and threat detection.
How to Choose the Right API Security Tool
The best choice depends on your environment and where your biggest API risks exist.
- Choose AccuKnox if your biggest gap is runtime visibility and protection for Kubernetes, microservices, and internal APIs.
- Choose Salt Security or Imperva if discovery and external API exposure monitoring are your top priorities.
- Choose 42Crunch if you want stronger API governance and CI/CD security testing.
- Choose Postman or Burp Suite if your focus is developer productivity or security testing depth.
- Choose Akamai, Apigee, or Kong if you need edge-scale delivery, gateway controls, or API program management alongside security features.
Conclusion

API security in 2026 requires layered protection across discovery, testing, and runtime enforcement. While many tools address individual stages of the API lifecycle, runtime protection has become essential as attackers increasingly exploit legitimate credentials and business logic rather than obvious vulnerabilities. Platforms like AccuKnox strengthen API security where attacks actually execute inside cloud-native environments helping organizations reduce API-driven risk without slowing development.
If you’re looking to secure APIs beyond the gateway and gain real runtime visibility inside Kubernetes, explore AccuKnox or schedule a demo to see runtime API security in action.
FAQs
What is the best API security tool in 2026?
The best API security tool in 2026 depends on your use case. For cloud-native runtime protection and internal API visibility, AccuKnox is a strong choice. For API discovery and behavioral analysis, Salt Security is widely considered. For design-time testing, 42Crunch is a strong fit.
Do API gateways provide enough API security?
No. API gateways are useful for authentication, routing, rate limiting, and basic policy control, but they do not fully address shadow APIs, business logic abuse, internal API communication, or runtime anomaly detection. Most teams need dedicated API security capabilities in addition to a gateway.
What features should I prioritize in an API security platform?
Look for continuous API discovery, OWASP API Top 10 testing, runtime behavior monitoring, zero-trust policy enforcement, CI/CD integration, and support for Kubernetes or cloud-native environments if you run microservices.
How should teams evaluate API security tools?
Teams should map tools to the API lifecycle design, build, and run and ensure there is clear coverage at runtime, where most real-world attacks occur.
Are gateway controls enough for API security?
No. API gateways and WAFs lack deep behavioral context and visibility into internal service-to-service APIs, making them insufficient on their own.
What makes runtime API security critical?
Most modern API attacks abuse valid functionality, such as authorization logic or data access patterns, which can only be reliably detected during execution.
How does AccuKnox differ from API gateways?
AccuKnox enforces zero-trust, behavior-aware API policies inside Kubernetes and cloud-native environments, extending protection beyond gateway boundaries.
What is full API visibility?
Every API endpoint: internal, external, documented, undocumented — known to your platform in real time, with zero sampling and continuous drift detection. Gateways, static scanning, and sampled traffic alone cannot achieve it.
What is a runtime API security checklist?
A structured set of evaluation criteria used to compare API security platforms based on how well they protect live production APIs — API discovery, behavioral detection, runtime policy enforcement, Kubernetes support, internal API visibility, and deployment complexity.
Ready to see runtime API security in action? Schedule a demo to explore how AccuKnox protects APIs at runtime.
Final Thoughts
API security in 2026 is no longer just about perimeter filtering. Modern attacks target the logic, identity, and runtime behavior of APIs, often using valid credentials and normal-looking traffic. That means organizations need layered protection across discovery, testing, and runtime enforcement.
If your environment is heavily cloud-native, API runtime security should be a top priority, especially for internal and east-west traffic that perimeter tools cannot see. By combining discovery, shift-left security, and runtime protection, teams can close the gaps that attackers increasingly exploit.
Get a LIVE Tour
Ready For A Personalized Security Assessment?
“Choosing AccuKnox was driven by opensource KubeArmor’s novel use of eBPF and LSM technologies, delivering runtime security”

Golan Ben-Oni
Chief Information Officer
“At Prudent, we advocate for a comprehensive end-to-end methodology in application and cloud security. AccuKnox excelled in all areas in our in depth evaluation.”
Manoj Kern
CIO
“Tible is committed to delivering comprehensive security, compliance, and governance for all of its stakeholders.”
Merijn Boom
Managing Director