


 Unified Zero Trust CNAPP


 Secure APIs
 Secure Kubernetes
 SIEM
 Secure Secrets


What Is API Security for Internal APIs? A Complete Guide + 7 Best Platforms in 2026


Internal APIs are the invisible nervous system of enterprise software — and they’re just as vulnerable as public-facing endpoints, often more so. This explainer and listicle covers what API security for internal APIs actually means, why it’s different from external API security, and the 7 best platforms built to protect APIs that never see the public internet but carry your most sensitive business data.
Reading Time: 13 minutes


Table of Contents


TL;DR
- Every API security tool on the market was built for north-south traffic — requests coming in from the outside world. None of them were built to watch your microservices talk to each other.
- The east-west blind spot is where lateral movement happens after a breach, where shadow APIs accumulate undetected, and where the OWASP API Top 10 plays out in slow motion.
- This guide covers what internal API security actually means, why gateways and WAFs are architecturally blind to it, and which 7 platforms come closest to solving the problem in 2026.
What Is Internal API Security?
Internal API security is the discipline of continuously discovering, authenticating, monitoring, and enforcing policy on APIs that operate exclusively within your private infrastructure — between microservices, across Kubernetes clusters, inside service meshes, and between the internal platform services that wire your product together.
The operative word is internal. These APIs never touch the public internet. They are not registered in your API gateway. They do not appear in your WAF logs. But they carry your most sensitive business logic — the calls from your payment service to your ledger service, from your auth layer to your session store, from your data pipeline to your analytics backend.
They are also the APIs your security team knows the least about.
Quick answer: Internal API security protects east-west, service-to-service API traffic inside private infrastructure such as Kubernetes clusters, service meshes, and internal platforms. Unlike external API security, it focuses on workload identity, lateral movement detection, shadow API discovery, and runtime enforcement for APIs that never pass through an API gateway.
Every API security tool on the market was built for north-south traffic — requests coming in from the outside world. None of them were built to watch your microservices talk to each other. The east-west blind spot is where lateral movement happens after a breach, where shadow APIs accumulate undetected, and where the OWASP API Top 10 plays out in slow motion.
This guide covers what internal API security actually means, why gateways and WAFs are architecturally blind to it, and which 7 platforms come closest to solving the problem in 2026.
Internal API security is not a subset of external API security. It is a different problem, requiring different tooling, different authentication primitives, and a fundamentally different threat model.
Internal vs. External API Security for Microservices: Why They Are Different Problems
Internal API security assumes the attacker is already inside. The threat model is lateral movement: a compromised pod, a misconfigured service account, or an over-privileged internal integration being used to hop from a low-sensitivity service to a high-sensitivity one. The attacker isn’t knocking at the door — they’re already in the building, opening internal doors you forgot existed.
| Dimension | External API Security | Internal API Security |
|---|---|---|
| Traffic direction | North-South (client → service) | East-West (service → service) |
| Primary threat | External attackers, bots, scrapers | Lateral movement, insider abuse, compromised workloads |
| Discovery method | Gateway inventory, spec catalog | Runtime traffic analysis, eBPF telemetry |
| Auth model | API keys, OAuth 2.0, JWT | mTLS, SPIFFE/SPIRE, service accounts |
| Where it breaks | Gateway bypass, token theft | Unmonitored east-west, over-permissioned service identity |
| Compliance evidence | Edge logs, WAF alerts | Runtime audit trails per workload identity |


The East-West Threat Model: What Actually Goes Wrong
East-west traffic is the lateral communication happening inside your infrastructure. In a Kubernetes cluster, it is every call your pods make to each other — and in a modern microservices architecture, that is thousands of calls per second across dozens of services, most of which are not governed, monitored, or even documented.
The three failure modes that turn east-west blind spots into incidents:
- Service impersonation — an attacker compromises a low-sensitivity pod and uses its service account to call internal APIs with elevated trust. Because there is no per-call authentication beyond the service account token, the call looks legitimate. Without workload identity validation at the call level, there is nothing to detect it.
- Privilege escalation via over-permissioned service accounts — a service that needs read access to a configuration API has been granted write access to a billing API. The misconfiguration existed for months. No one noticed because east-west traffic was never audited. One compromised pod exploits it.
- Shadow API lateral movement — a deprecated internal endpoint was removed from the spec, but never from the routing table. An attacker discovers it through internal enumeration — a technique that is trivial east-west and impossible to detect without runtime traffic analysis.
These are not theoretical attack paths. They are the patterns that appear in post-incident reviews after breaches where the attacker was already inside.’ The question is never whether east-west APIs are at risk — it is whether you have any visibility when they are abused.

Why API Gateways and WAFs Are Architecturally Blind to Internal APIs
This is the most important structural point in the guide, and it is the reason dedicated internal API security tooling exists at all.
API gateways are designed to manage the boundary between the outside world and your internal services. They are excellent at what they were built for: standardizing authentication, enforcing rate limits, routing external traffic, and providing a developer-facing catalog. But they have three properties that make them structurally blind to internal API security:
- They only see managed traffic. Any service that calls another service directly — via internal DNS, Kubernetes service discovery, or a service mesh sidecar — bypasses the gateway entirely. In most Kubernetes environments, the majority of API calls never touch the gateway.
- They authenticate requestors, not workloads. A gateway can verify a JWT or API key. It cannot verify that the specific Kubernetes pod presenting that credential is the legitimate process it claims to be. Workload identity — the ability to cryptographically prove that a specific container in a specific cluster is making a call — requires a different layer.
- They operate at L7, not the kernel. A compromised process can make internal API calls that bypass any application-layer control. Detecting and blocking those calls requires observability at the system call level — which means eBPF, not a gateway.

How Internal API Discovery Works in 2026: Methods Comparison for East-West API Visibility
No single method provides complete coverage. The gap between ‘what your gateway knows about’ and ‘what is actually live and reachable’ is where internal API risk accumulates.
| Method | What It Sees | What It Misses | Internal API Fit |
|---|---|---|---|
| API Gateway | Managed ingress/egress — documented paths | Bypass routes, service mesh, east-west calls, internal DNS | Structural blind spot for internal APIs |
| WAF | Edge request patterns and payloads | Everything behind the perimeter — all east-west traffic | No east-west coverage at all |
| Service Mesh | L7 service-to-service with mTLS and identity | Services not yet on the mesh — partial adoption is common | Good coverage was deployed |
| eBPF | Kernel-level API calls, real workload identity, process context | Requires kernel access — not available on all managed cloud node types | Best fit — runtime truth without gateway dependency |
| OpenAPI / Spec | Documented endpoints, spec drift from live traffic | Undocumented internal APIs — the worst ones | Useful as a baseline, not a discovery source |
The win condition is correlated discovery: traffic analysis + eBPF telemetry + service mesh signals + spec drift detection, normalized into one live inventory that updates at the save your Kubernetes environment changes.
mTLS, SPIFFE, and SPIRE: The Authentication Baseline for Internal APIs
External APIs authenticate requestors — the entity making the call. Internal APIs need to authenticate workloads — the specific process, pod, or service making the call, independent of the credentials it presents.
That is why mTLS, SPIFFE, and SPIRE have become the baseline design pattern for internal API security in cloud-native environments:
- mTLS encrypts service-to-service traffic and enables mutual authentication between workloads.
- SPIFFE provides a standard identity format for workloads.
- SPIRE issues and manages those workload identities in dynamic environments like Kubernetes.
Together, they give security teams a way to answer the question that matters most in east-west traffic: which workload made this call, from where, and should it have been allowed?
Mutual TLS (mTLS) is the transport-layer foundation. Unlike standard TLS, where only the server presents a certificate, mTLS requires both sides to present and validate certificates. This means a service cannot call another internal service without proving its identity at the TLS layer — closing the impersonation attack surface.
SPIFFE (Secure Production Identity Framework for Everyone) and SPIRE (its runtime reference implementation) take this further by providing a cryptographic workload identity that is independent of IP addresses, which are unreliable in Kubernetes environments where pods are rescheduled continuously. Every workload receives a SPIFFE Verifiable Identity Document (SVID) — a short-lived, cryptographically signed credential tied to the workload’s identity in the platform, not its network location.
The practical implication: mTLS + SPIFFE/SPIRE means a compromised pod cannot impersonate another service, because it cannot forge the SVID of the service it is trying to impersonate. Authorization decisions become workload-identity-aware rather than IP-or-token-aware.
Platforms that cannot integrate with or enforce mTLS and SPIFFE/SPIRE are operating without workload identity in their internal API security model. That is a structural gap — not a feature gap.

The 7 Best API Security Platforms for Internal APIs in 2026
The market for internal API security is genuinely nascent — most vendors claim coverage but were built for external APIs and retrofitted. This ranking evaluates platforms on criteria that matter for east-west, Kubernetes-native environments: eBPF or equivalent kernel-level visibility, workload identity integration, mTLS/SPIFFE support, and deployment flexibility beyond SaaS-only.
| Platform | East-West Visibility | K8s Native | mTLS / SPIFFE | Deployment Flexibility | PCI / HIPAA Audit |
|---|---|---|---|---|---|
| AccuKnox | eBPF kernel-level, no gateway required | KubeArmor — workload-identity-aware | mTLS + SPIFFE/SPIRE native | SaaS / On-prem / Air-gap / Hybrid | Continuous — 30+ frameworks |
| Salt Security | Limited — SaaS traffic analysis | Partial | Partial | SaaS only | Moderate |
| Noname Security | Posture-focused, not runtime | Partial | Limited | SaaS / Hybrid | Moderate |
| Traceable AI | Distributed tracing, app-layer only | Partial | Limited | SaaS only | Limited |
| Imperva | Perimeter-first architecture | Limited K8s native coverage | Partial | Hybrid | Strong — PCI/HIPAA mature |
| Wiz | Detection only — no enforcement | Cloud graph with K8s context | Limited | SaaS only | Moderate |
| F5 NGINX | Gateway-level only — bypass blind spot | Infra-focused, not workload-aware | mTLS at proxy layer | On-prem / Cloud | Good |
1. AccuKnox — Only Platform With Kernel-Level East-West Enforcement: AccuKnox is the only platform combining full CNAPP with kernel-level east-west API enforcement via eBPF — no gateway or service mesh required. KubeArmor provides workload-identity-aware policy inside Kubernetes clusters, knowing exactly which pod and process made each API call. mTLS and SPIFFE/SPIRE integration closes service impersonation at the kernel level. PCI DSS v4.0.1 compliance evidence is generated continuously from live workload activity. Deployment spans SaaS, on-premises, hybrid, and air-gapped environments.

The differentiator no competitor can replicate: eBPF-based east-west observability enforced at the kernel validated in KubeArmor and independent CWPP analysis.
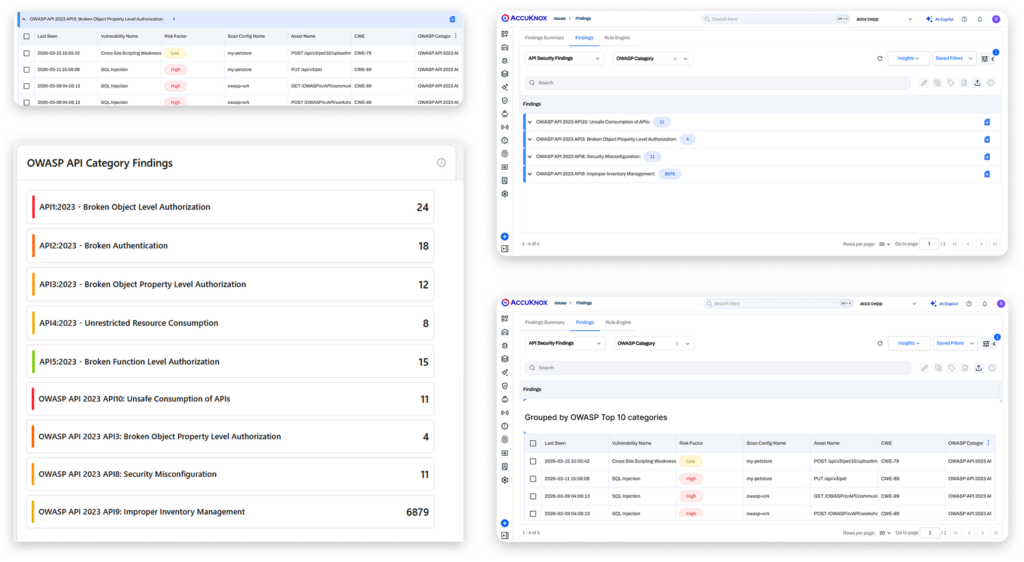
AccuKnox Provides Visibility on OWASP Top 10 Findings for API Security
2. Salt Security AI-powered behavioral baselines detect slow-moving abuse patterns across internal API ecosystems that rule-based tools miss. Strong detection where gateways are present — though being SaaS-only means east-west traffic must leave your environment for analysis, making it a difficult fit for regulated or air-gapped deployments.
3. Noname Security Best-in-class API inventory and ownership governance across distributed teams — flags spec drift, maps API lifecycle, and routes findings to the right owners. Where it stops short is at execution: east-west traffic is classified and reported, but active runtime enforcement requires bringing in additional tooling.
4. Traceable AI Distributed tracing delivers deep request-level observability across internal microservice calls — a natural fit for teams already on OpenTelemetry. Multi-step API abuse patterns are detected with precision. The scope, however, stays at the application layer — workload identity governance and kernel-level east-west enforcement fall outside what it was built to do.
5. Imperva Mature PCI DSS and HIPAA compliance reporting with audit workflows that enterprise teams recognize. Works well where internal APIs consistently route through managed Imperva infrastructure — though in most Kubernetes environments, the majority of east-west traffic bypasses that managed path entirely, leaving it unmonitored.
6. Wiz Security graph connects internal API exposure to cloud configuration, identity entitlements, and K8s posture — the strongest risk contextualization in this category. The platform is built to surface and prioritize risk, not act on it, so blocking an active east-west exploit still depends on a separate enforcement layer.
7. F5 NGINX Consistent mTLS enforcement and API policy at the proxy layer for NGINX-standardized environments. Sidecar deployment provides genuine east-west coverage where it’s been rolled out — the visibility, however, ends at the mesh boundary, leaving direct pod-to-pod calls and services not yet onboarded completely outside its view.
Match Your Environment to the Right Internal API Security Approach
The right approach depends on where your APIs live and how your teams operate — not on feature checklists. Use this to identify your primary requirement before evaluating any tool.
| Your Situation | What Actually Matters |
|---|---|
| K8s-native microservices, heavy east-west | eBPF runtime + workload identity, no gateway dependency |
| HIPAA / PCI DSS mandate | Continuous audit trails, behavioral detection, and evidence automation |
| Service mesh (Istio / Envoy / Cilium) | mTLS enforcement + SPIFFE/SPIRE workload identity |
| Multi-team API sprawl | Ownership mapping, inventory governance, drift alerts |
| Air-gapped or sovereign-cloud infra | On-prem / air-gap deployment with full feature parity |
| Cloud posture + API risk in one view | CNAPP-correlated API exposure with cloud config context |
Internal API Security Checklist for Kubernetes and Service Mesh Environments
If you are evaluating internal API security platforms, these are the highest-signal capabilities to look for:
- Runtime discovery of undocumented internal APIs
- Workload identity enforcement tied to pod, service account, and cluster context
- East-west traffic visibility beyond ingress controllers and API gateways
- Detection of shadow APIs and deprecated but reachable endpoints
- Per-call audit trails for compliance and incident response
- Support for mTLS and SPIFFE/SPIRE-based identity
- Runtime policy enforcement at the workload or kernel layer
- Coverage for partial service mesh adoption, not just mesh-only environments
A platform does not need to do all of these perfectly, but if it cannot see service-to-service traffic or validate workload identity, it is not truly solving internal API security.
From Zero to Internal API Visibility: An 8-Step Operational Runbook
Buying the right platform is step one. Operationalizing internal API security is the part most teams underestimate. This runbook reflects the sequence that works in practice.
Baseline your east-west traffic. Deploy eBPF or service mesh telemetry to capture real east-west API calls — not just what your gateway logs. This is your ground truth.
Build a live internal API inventory. Deduplicate endpoints across signals, tag north-south vs east-west exposure, and link each endpoint to a namespace, cluster, and owning team.
Identify shadow APIs, zombie APIs, and orphan APIs. Shadow = live but unregistered. Zombie = deprecated but still routable. Orphan = no current owner. These three categories are your highest-risk internal APIs.

Classify sensitivity and criticality. Tag endpoints handling PII, PHI, or financial data. Score by business criticality (customer-facing, revenue-path, internal platform, admin/control plane).
Apply workload identity and mTLS. Enforce SPIFFE/SPIRE SVIDs for service-to-service authentication. Deploy mTLS for all east-west calls. This closes service impersonation as an attack path.
Set least-privilege authorization baselines. For each internal API, define which services should be able to call it and under what conditions. Block everything else — including legitimate services that have no documented need.
Monitor for east-west abuse patterns. Enable runtime anomaly detection for BOLA patterns, over-permissioned service calls, enumeration behavior, and authZ drift. Tune thresholds using workload-identity-correlated signals.
Automate audit evidence collection. Route findings to your SIEM and ticketing system. Generate compliance evidence continuously — tied to live API behavior, not periodic scans.

Frequently Asked Questions
What is the difference between internal API security and API gateway security?
API gateway security focuses on north-south traffic entering or leaving your environment. Internal API security focuses on east-west traffic between workloads inside your infrastructure. The core difference is visibility and trust model: gateways protect the edge, while internal API security protects service-to-service calls after an attacker is already inside.
How do you discover shadow internal APIs in Kubernetes?
The most effective approach is runtime-based discovery using traffic analysis, eBPF telemetry, service mesh signals, and comparison against your OpenAPI specs. Spec-only inventories miss undocumented endpoints, while gateway-based inventories miss direct pod-to-pod communication.
Is mTLS enough to secure internal APIs?
No. mTLS is necessary, but not sufficient. It encrypts traffic and helps authenticate workloads, but it does not by itself provide full API discovery, behavior monitoring, authorization validation, or runtime detection of abuse and lateral movement.
Get a LIVE Tour
Ready For A Personalized Security Assessment?
“Choosing AccuKnox was driven by opensource KubeArmor’s novel use of eBPF and LSM technologies, delivering runtime security”

Golan Ben-Oni
Chief Information Officer
“At Prudent, we advocate for a comprehensive end-to-end methodology in application and cloud security. AccuKnox excelled in all areas in our in depth evaluation.”

Manoj Kern
CIO
“Tible is committed to delivering comprehensive security, compliance, and governance for all of its stakeholders.”

Merijn Boom
Managing Director


