


 Unified Zero Trust CNAPP


 Secure APIs
 Secure Kubernetes
 SIEM
 Secure Secrets


AI Security Posture Management for LLMs & Agents
Discover every model, agent, and pipeline. Close gaps across 43 compliances. Auto-generate your AI Bill of Materials.
Schedule a Demo
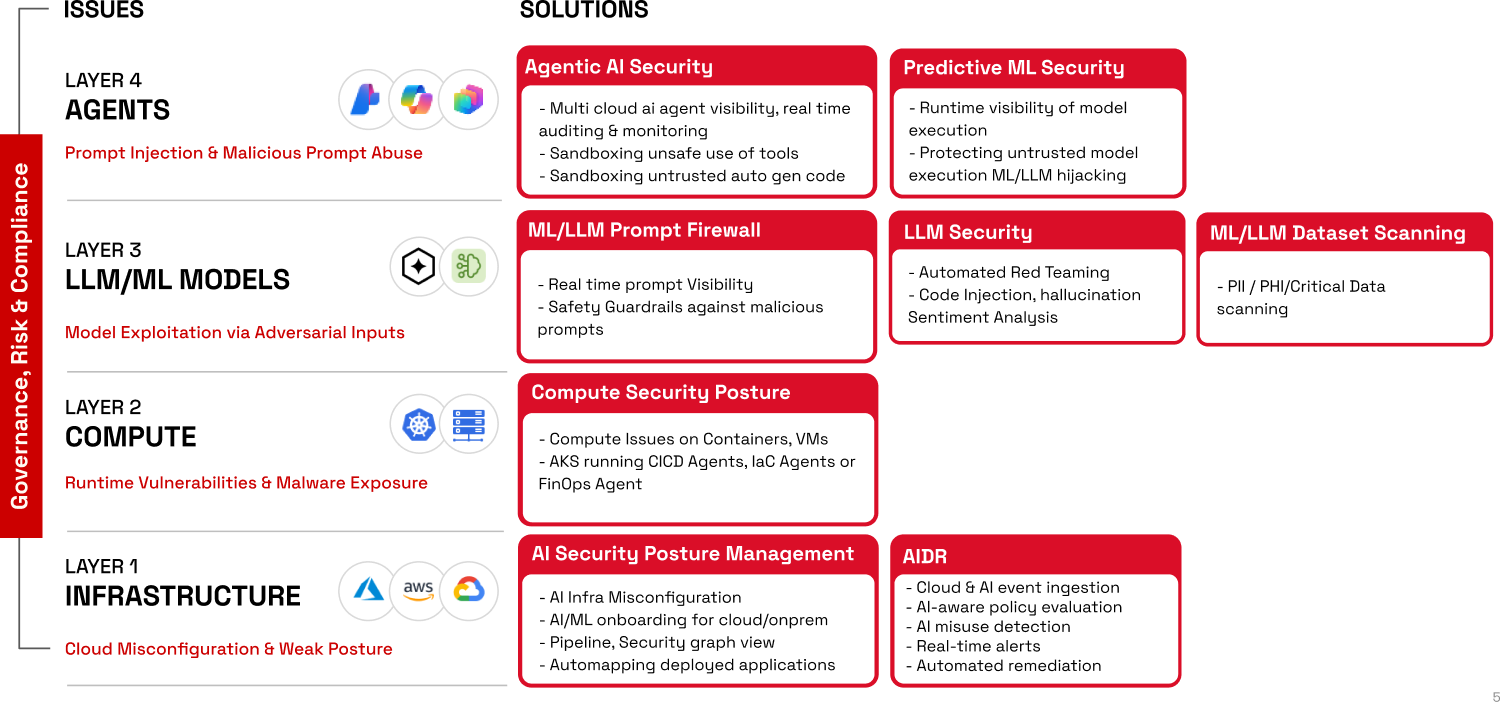
Your AI stack breaks in eight places.
Eight fronts covered. Zero blind spots.


- No inventory of models, agents, datasets, pipelines
- Shadow AI deploys where nobody is looking
- Open endpoints on Bedrock & Azure OpenAI
- Live inventory, agentless, one dashboard
- Shadow AI discovery for notebooks & MCP servers
- Auto-remediates exposures the instant they appear


- Overnight deploys with nobody watching
- Chained attacks look harmless step by step
- Scattered incidents across disconnected tools
- Continuous ingest of CloudTrail, Azure, GCP logs
- Full attack path rebuilt from weak signals
- Auto-routes to Jira, ServiceNow, Slack, PagerDuty


- Hijacked agents touch files & networks off-limits
- Tool abuse and rogue API calls
- Poisoned memory corrupts reasoning over time
- Runtime sandbox via eBPF & LSM, no code changes
- Least privilege tool access, blocked before it runs
- Catches poisoning before a decision changes


AI Model & Dataset Security

- Hidden malware in Pickle, HDF5, ONNX files
- Poisoned models from Hugging Face & GitHub
- Unscanned PII/PHI buried in training data
- Scans 5 formats for tampering & deserialization
- Blocks poisoned models before they deploy
- Maps findings to OWASP LLM Top 10 & MITRE ATLAS


- Yearly pen tests can't match weekly updates
- Generic tools miss jailbreaks & encoding tricks
- Silent regressions after every fine-tune
- 150+ probes fire on every model change
- Real attacker TTPs, mapped to OWASP & MITRE
- Custom probe packs for domain-specific risk


AI Identity Security
- Shared API keys across every agent
- No per-agent permissions or scoping
- Impersonation of trusted agents
- SPIFFE identity unique to every agent
- Per-agent permissions, enforced automatically
- Blocks spoofing with cryptographic attestation


- Slow jailbreaks spread across 5-15 messages
- Leaked secrets: PII, PHI, credentials in prompts
- Fragmented setup per channel
- Stateful engine tracks the whole conversation
- Real-time masking of PII, PHI & secrets
- One policy across gateway, SDK, browser, Copilot


- Weeks of mapping to OWASP, NIST, EU AI Act by hand
- Proof, not slides is what auditors want
- 12+ frameworks to satisfy at once
- Auto-tags findings to 12+ frameworks
- Per-query trail auditors can actually verify
- On-demand reports, SaaS or air-gapped

8 Modules, Tightly Integrated, Loosely Coupled

Al Security Platform
Secure Every Al Asset. Protect Every Layer. Click To View
-

Security Posture Management
-

Model & Dataset Security
-

Agentic AI Security
-

Detect & Respond
-

Governance, Risk & Compliance
-

Guardrails & Prompt Firewall
-

Identity Security
-

Red Teaming & Pen Testing

AI Assets

Agents

Models

Knowledge Base

Tools

Substrate

Infra

Application

Data

Network

Deployments
Public Cloud
Private Cloud

Air-Gapped

Edge/IoT
AI Security Posture Management (AI SPM)
- Builds a live, agentless inventory of every model, agent, dataset, and pipeline, spanning cloud and on-prem, in one dashboard.
- Shadow AI discovery catches unapproved notebooks, rogue models, and MCP servers automatically.
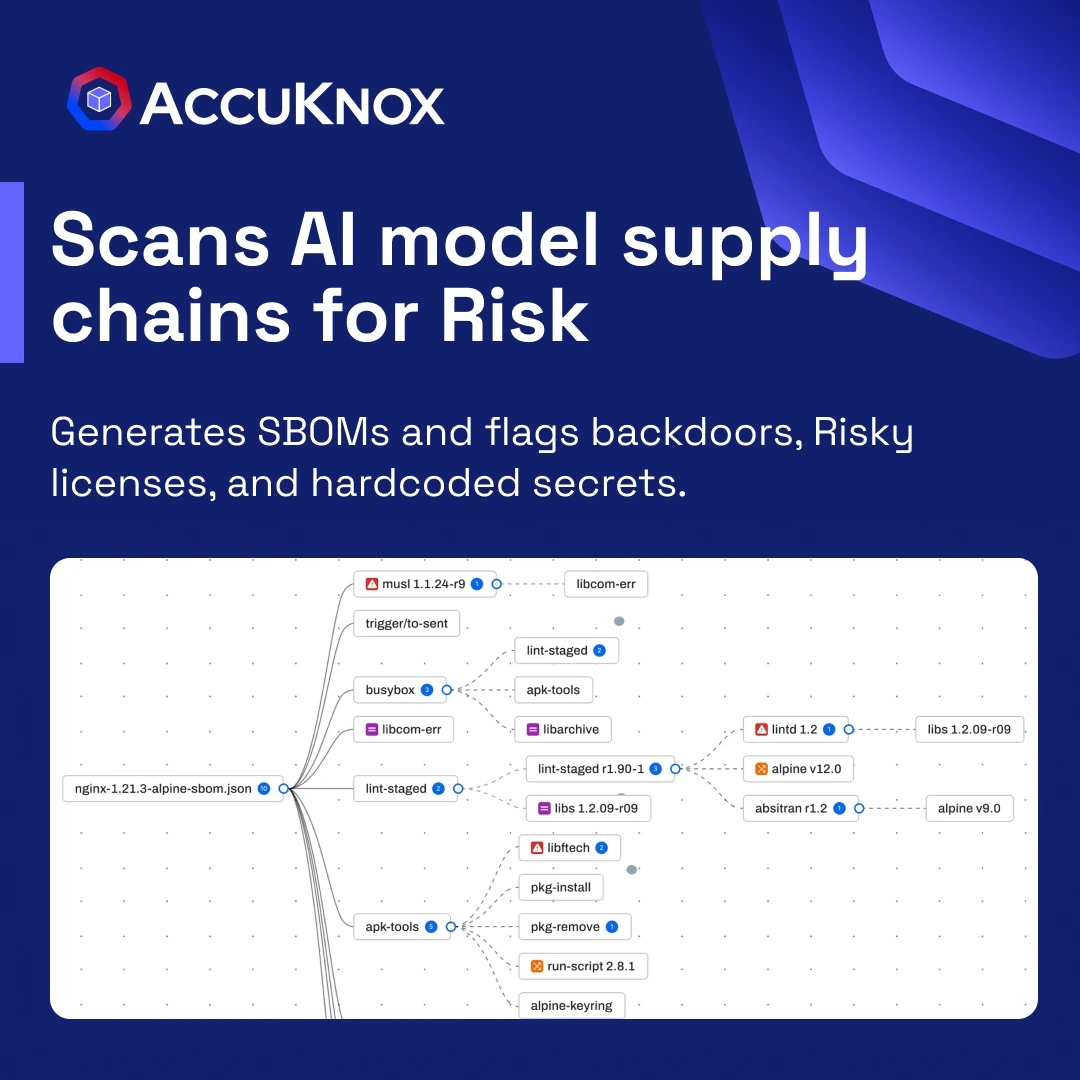
- Generates an AI Bill of Materials per model and agent, with EU AI Act risk tiering built in.
- Auto-remediates exposed endpoints the instant they're found, no ticket required.

AI Model, Dataset Security
- Scans all 5 major model formats for supply-chain tampering and deserialization attacks.
- Flags integrity violations in public Hugging Face or GitHub models before deployment.
- Scans training datasets for PII/PHI before it becomes a compliance incident.
- Re-scans automatically on every fine-tune, tagged to OWASP LLM Top 10 and MITRE ATLAS.

Agentic AI Security
- Sandboxes every agent at runtime with eBPF and LSM enforcement, no code changes needed.
- Enforces least-privilege tool access and blocks unauthorized calls before they execute.
- Detects memory poisoning and cascading hallucination before they corrupt a decision.
- Real-time, multi-cloud visibility into every agent running across AWS, Azure, GCP, and on-prem.

AI Detect and Respond (AI DR)
- Continuously ingests AWS, Azure, and GCP logs, catching unapproved deployments the moment they happen.
- Correlates signals across layers to reconstruct full, multi-step attack chains.
- Makes exposed model endpoints private automatically, no manual fix needed.
- Routes every incident straight into Jira, ServiceNow, Slack, or PagerDuty with full forensic context.

AI Compliance and Governance (AI GRC)
- Auto-tags every finding to OWASP, MITRE ATLAS, NIST AI RMF, and the EU AI Act.
- Classifies EU AI Act risk tier the moment a model is discovered.
- Generates audit-ready reports on demand, no more weeks of manual evidence-gathering.
- Proves governance across 12+ frameworks from a single dashboard, SaaS or air-gapped.

AI Guardrails, Stateful Prompt Firewall
- Stateful engine tracks entire conversations, catching jailbreaks that unfold over 5-15 messages.
- Masks PII, PHI, and credit card numbers in real time, before they reach the model.
- Detects and blocks leaked API keys, passwords, and credentials instantly.
- One policy enforced everywhere: API gateway, SDK, browser plugin, and Copilot Studio.

AI Identity Security
- Gives every agent its own verifiable, cryptographic identity via SPIFFE, no shared keys.
- Enforces fine-grained, per-agent permissions automatically.
- Tracks the full upstream caller chain before granting access.
- Blocks impersonation with cryptographic attestation, identity that can't be faked.

AI Red Teaming, Pen Testing
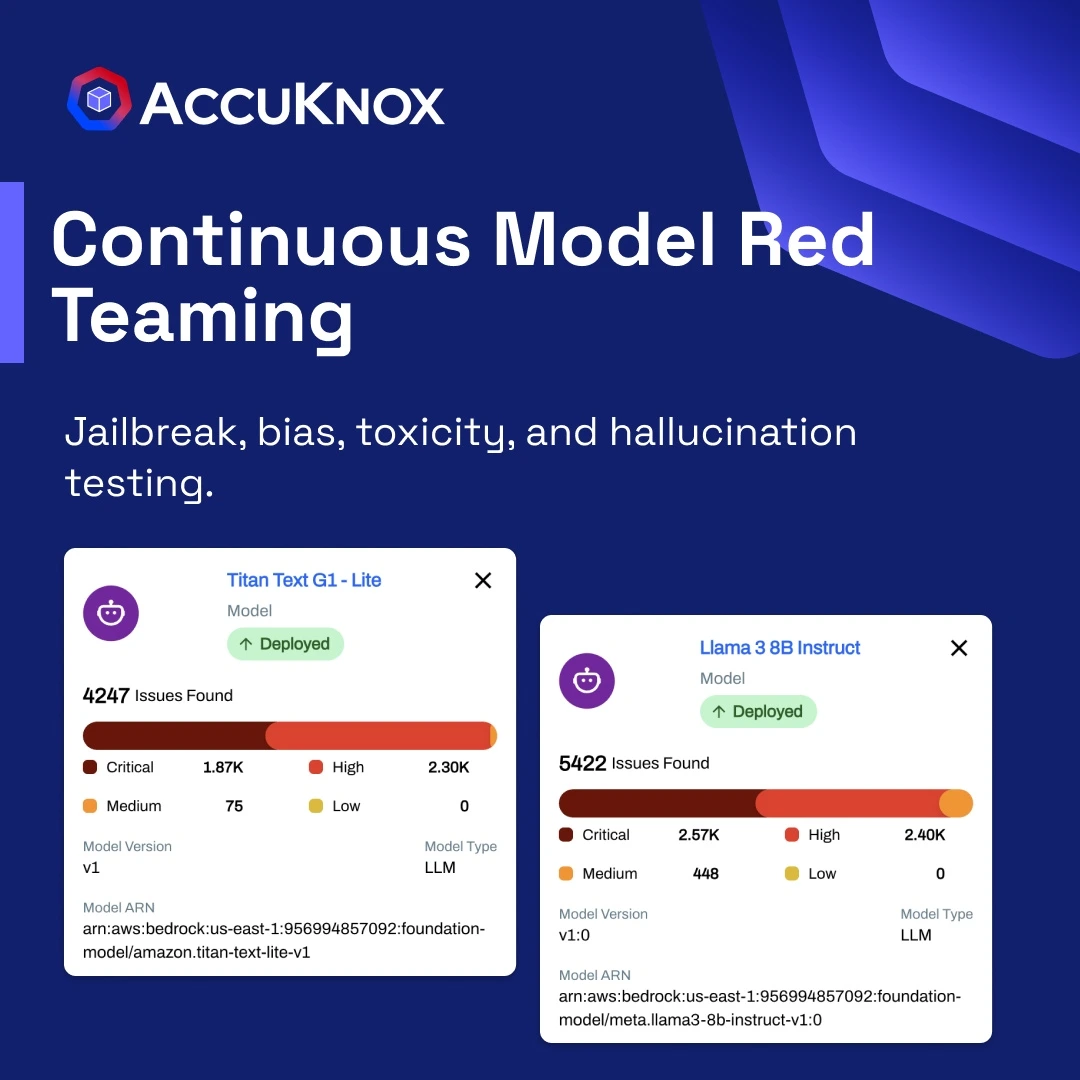
- Runs 150+ adversarial probes automatically, triggered on every model change.
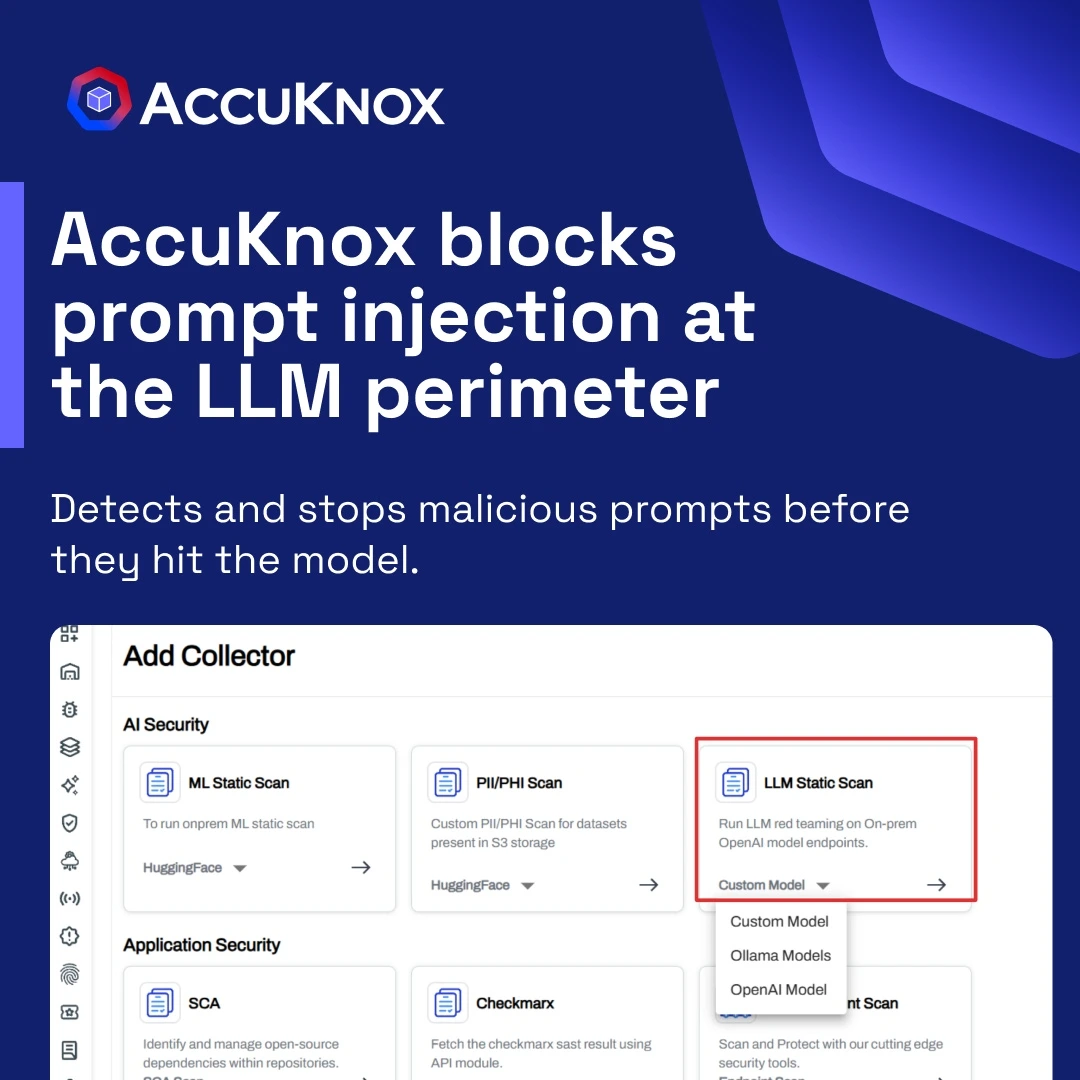
- Tests with real attacker techniques: jailbreaks, encoding attacks, prompt injection.
- Hallucination detection catches fabricated packages or false facts before users see them.
- Custom, domain-specific probe packs for finance, healthcare, and beyond.

AI Security Platform Tour
(Models, Agents, MCPs, SDKs)
- Inventory View
- AI Model View
- Managed Agents View
- Shadow AI Discovery
- Prompt Firewall Dashboard
- Runtime Defense
- Runtime Agent Sandboxing
- AI Compliance
Inventory View (List)
Asset sprawl across cloud, network, and API layers means no single source of truth for what is exposed and how it is configured.
AI Assets Covered
AI Models, Datasets, Compute Resources, Bedrock, SageMaker, Vertex AI, Azure AI, and cloud AI services.
Security Outcomes
AI Asset Inventory, AI Security Posture Management (AI-SPM), risk visibility, ownership tracking, and exposure management.

Risk View from Red Teaming
Per-model risk view from automated red team scans, with findings broken down across four attack categories: code, hallucination, prompt injection, and sentiment analysis. Each category lists severity counts and specific test cases.
Security Tests
Prompt Injection, Hallucination Detection, Jailbreak Testing, Unsafe Code Generation, and adversarial robustness validation.
Framework Mapping
OWASP Top 10 for LLMs, MITRE ATLAS, Model Security Scoring, and risk-based remediation.

Managed Agents View
Managed agent inventory filtered by cloud provider, with a detail pane for agent metadata, memory configuration, deployment timeline, and risk finding counts by severity.
Agent Coverage
Amazon Bedrock Agents, Azure AI Agents, Copilots, Custom Agent Frameworks, and enterprise agent deployments.
Operational Visibility
Agent Memory, Tool Usage, Knowledge Bases, Deployment Lifecycle Monitoring, and runtime risk insights.

Inventory View (List)
Shadow AI discovery lists unmanaged assets by category: AI agents, AI gateways, AI inference engines, AI-ML libraries, AI SDKs, and MCP servers. Each category shows asset count and associated findings.
Shadow AI Detection
MCP Servers, AI SDKs, AI Gateways, Inference Engines, AI/ML Libraries, and unknown AI assets.
Discovery Insights
Software Provenance, License Tracking, Security Findings, Asset Ownership, and dependency visibility.

AccuKnox Prompt Firewall Dashboard
Prompt the firewall dashboard with top policy violations by policy name and by application, failure counts by severity, and a full application inventory with violation trends and owner attribution.
Threat Detection
Prompt Injection, Secrets Exposure, PII Leakage, Toxicity Violations, and unsafe prompt activity.
Runtime Controls
Prompt Firewall, AI Gateway Enforcement, Response Filtering, Policy Analytics, and usage monitoring.

Runtime Defense Prompt Policies
Prompt policy library with 10 policy types: anonymisation, gibberish detection, prompt injection, toxicity, competitor mentions, topic bans, code filtering, language enforcement, regex sanitisation, secrets detection, and token limits.
Policy Library
Anonymization, Secrets Detection, Toxicity Controls, Code Restrictions, Token Limits, and language enforcement.
AI Guardrails
Runtime Enforcement, Responsible AI Controls, Content Governance, Risk Reduction, and policy compliance.

Runtime Agent Sandboxing
KubeArmor runtime sandboxing for AI agents with auto-discovered and custom policies. Each policy enforces process, filesystem, credential, and network isolation at the K8s workload level via zero-trust YAML.
Zero Trust Controls
Process Isolation, Filesystem Protection, Network Segmentation, Credential Security, and execution control.
Protected Workloads
AI Agents, MCP Servers, Inference Engines, Kubernetes Agentic AI Environments, and autonomous workflows.

AI Compliance, Attack Frameworks
Compliance framework selector with 12 active standards: OWASP Top 10 for LLMs, MITRE ATLAS, NIST 800-171, HIPAA, ISO 27001, SOC 2, PCI, RBI CSF, HITRUST CSF, GDPR, ISO 27017, and NIST SP 800-53.
Compliance Standards
OWASP LLM Top 10, MITRE ATLAS, NIST AI RMF, ISO 27001, SOC 2, GDPR, and HIPAA.
Governance Coverage
AI Models, Agents, Datasets, Prompts, Infrastructure, Audit Readiness, and control validation.

Book a Demo

- Flexible AI Deployments
- Support Matrix
- Security Across Layers
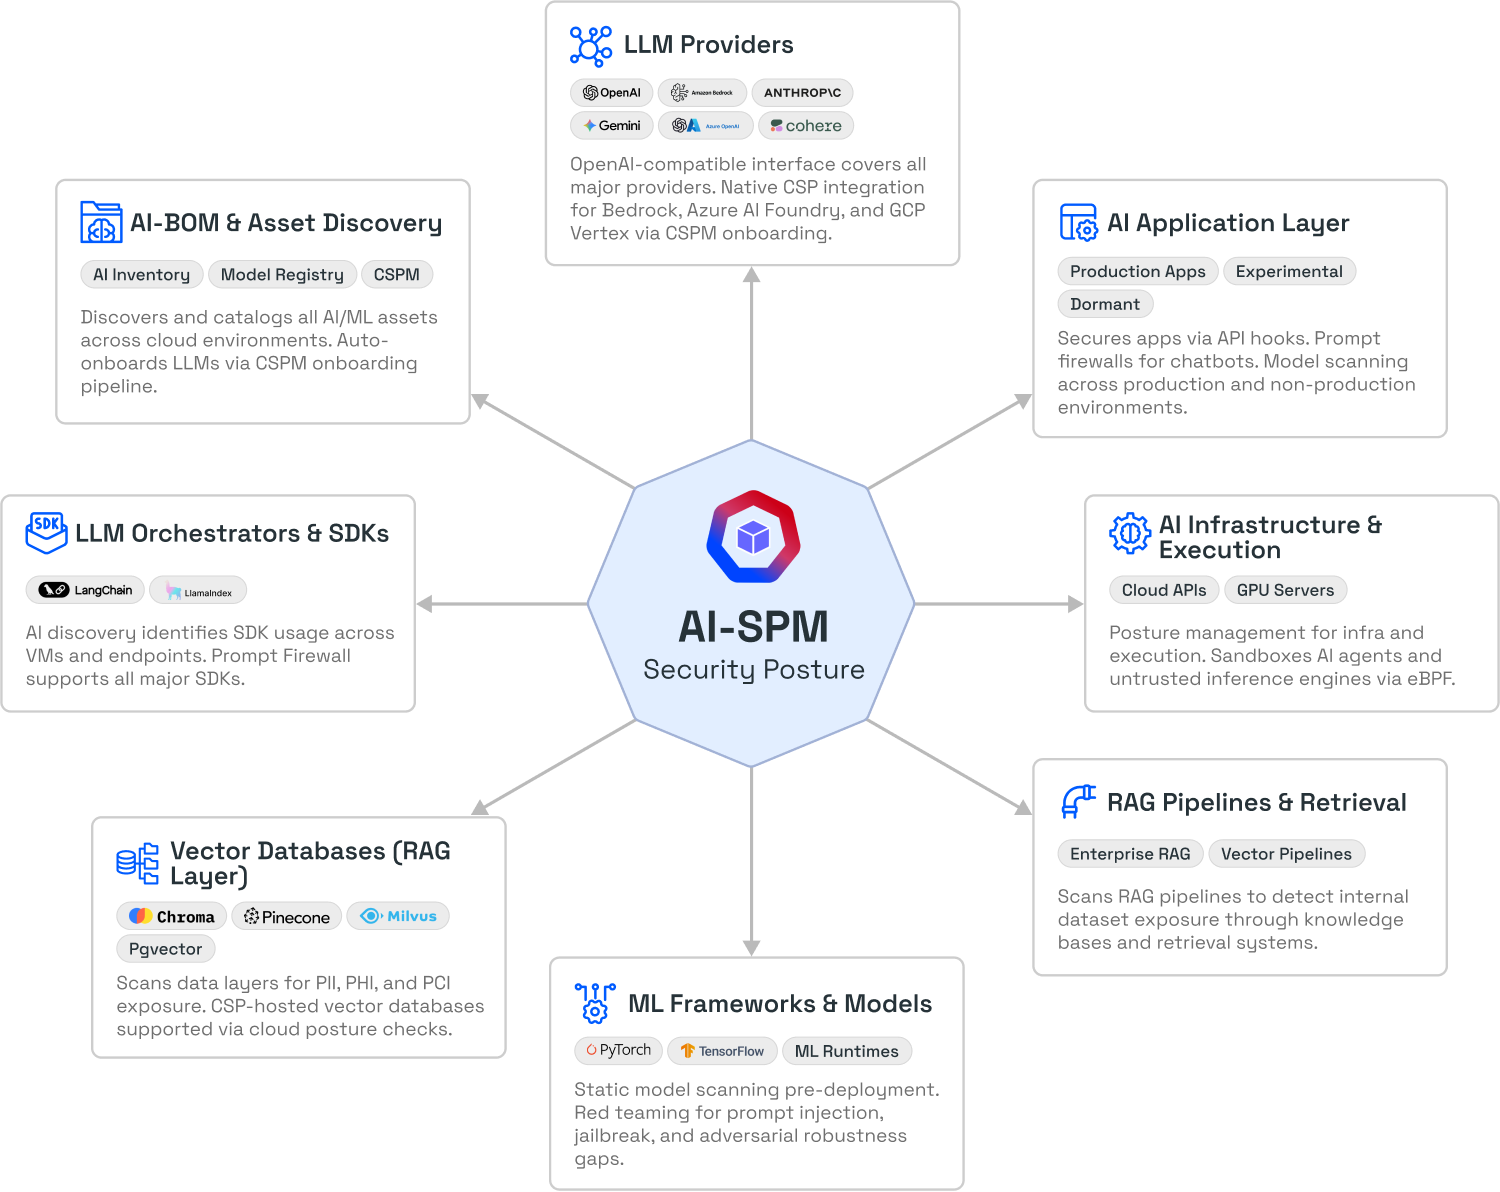
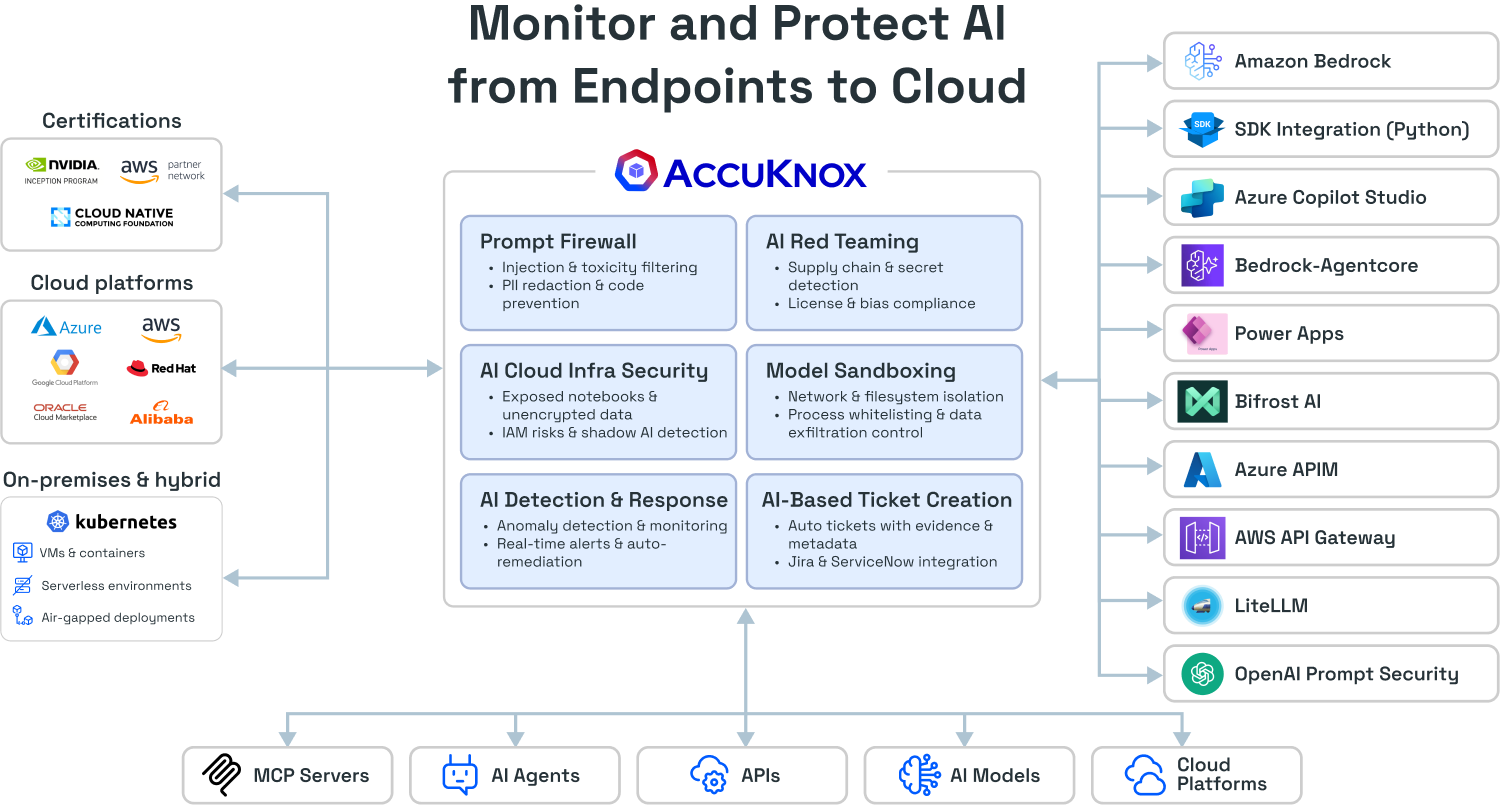
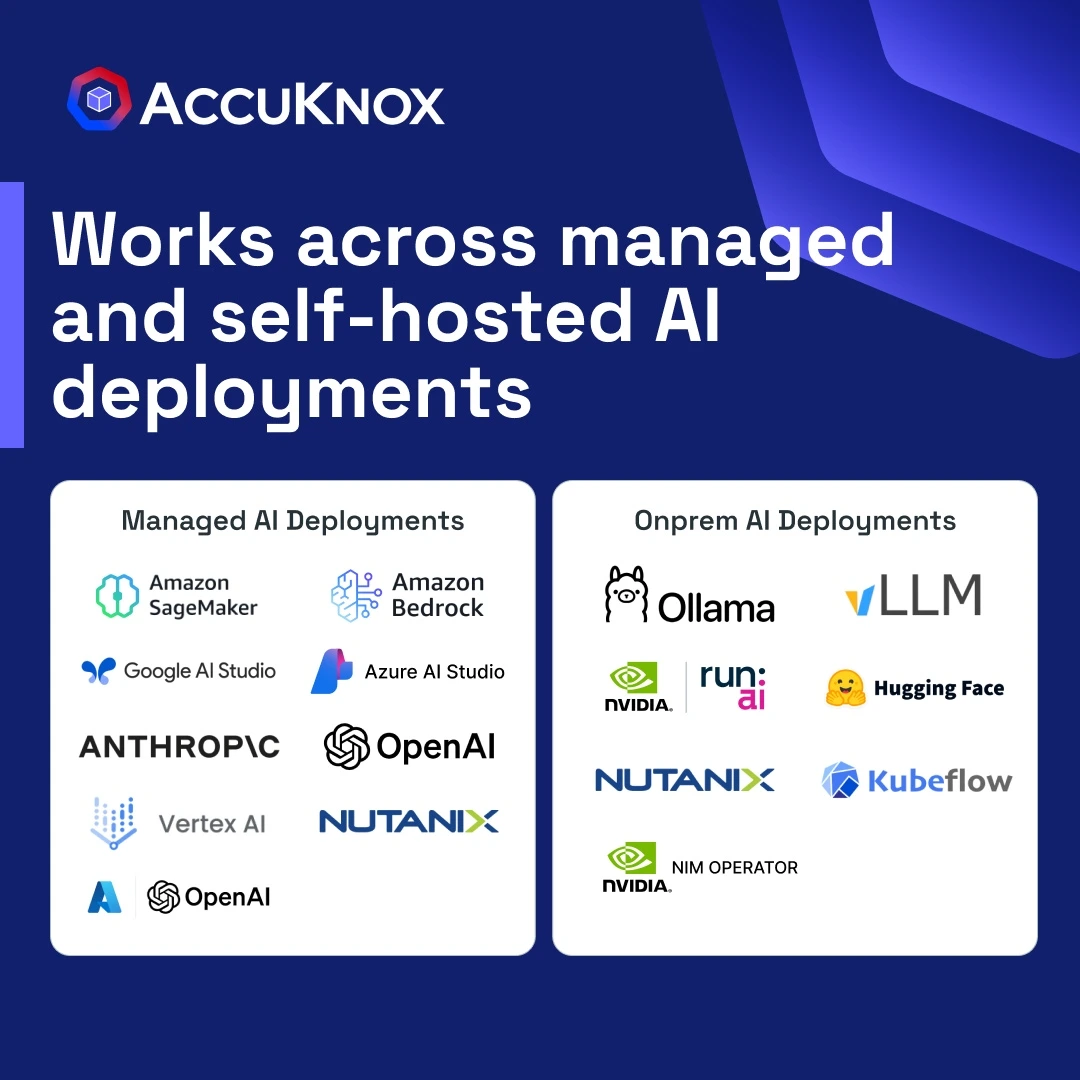
How AccuKnox Connects to Your AI Assets – Agentless by Default

AI-SPM – SaaS & On-Prem Deployment
Same powerful protection. Choose the deployment that fits your infrastructure, data-residency, and compliance needs.

AI Agent Security Across Multi-Cloud Platforms
Real-time visibility, sandboxing, and auditing for AI agents across Azure AI Foundry, Copilot Studio, and AWS Bedrock.

Multi-Cloud Agent Visibility & Auditing
Continuous discovery, behavioral auditing, and risk monitoring of AI agents across cloud environments.

Sandbox Unsafe Tool Usage
Prevents agents from executing risky external tools, APIs, and actions in runtime workflows.

Sandbox Auto-Generated Code
Isolates LLM-generated scripts and code execution to prevent malicious runtime behavior.

Multi-Platform Support
Industry-first agent discovery and governance across major cloud platforms.
AI Model Cards for Continuous Governance
Transform your model documentation from static reports into a real-time security and risk dashboard.
- Continuous Security & Supply Chain
Get a live Software Bill of Materials (SBOM), real-time vulnerability scanning, and ongoing license compliance checks for all model components. - Automated Validation & Risk Scoring
Use sandbox-driven assessments for automated red teaming, evaluating safety, bias, toxicity, jailbreak resilience, and assigning a dynamically changing risk score. - Runtime Observability & Fencing
Establish behavior baselines and monitor operational activity to detect policy violations and ensure real-time data isolation and fencing of model data stores.

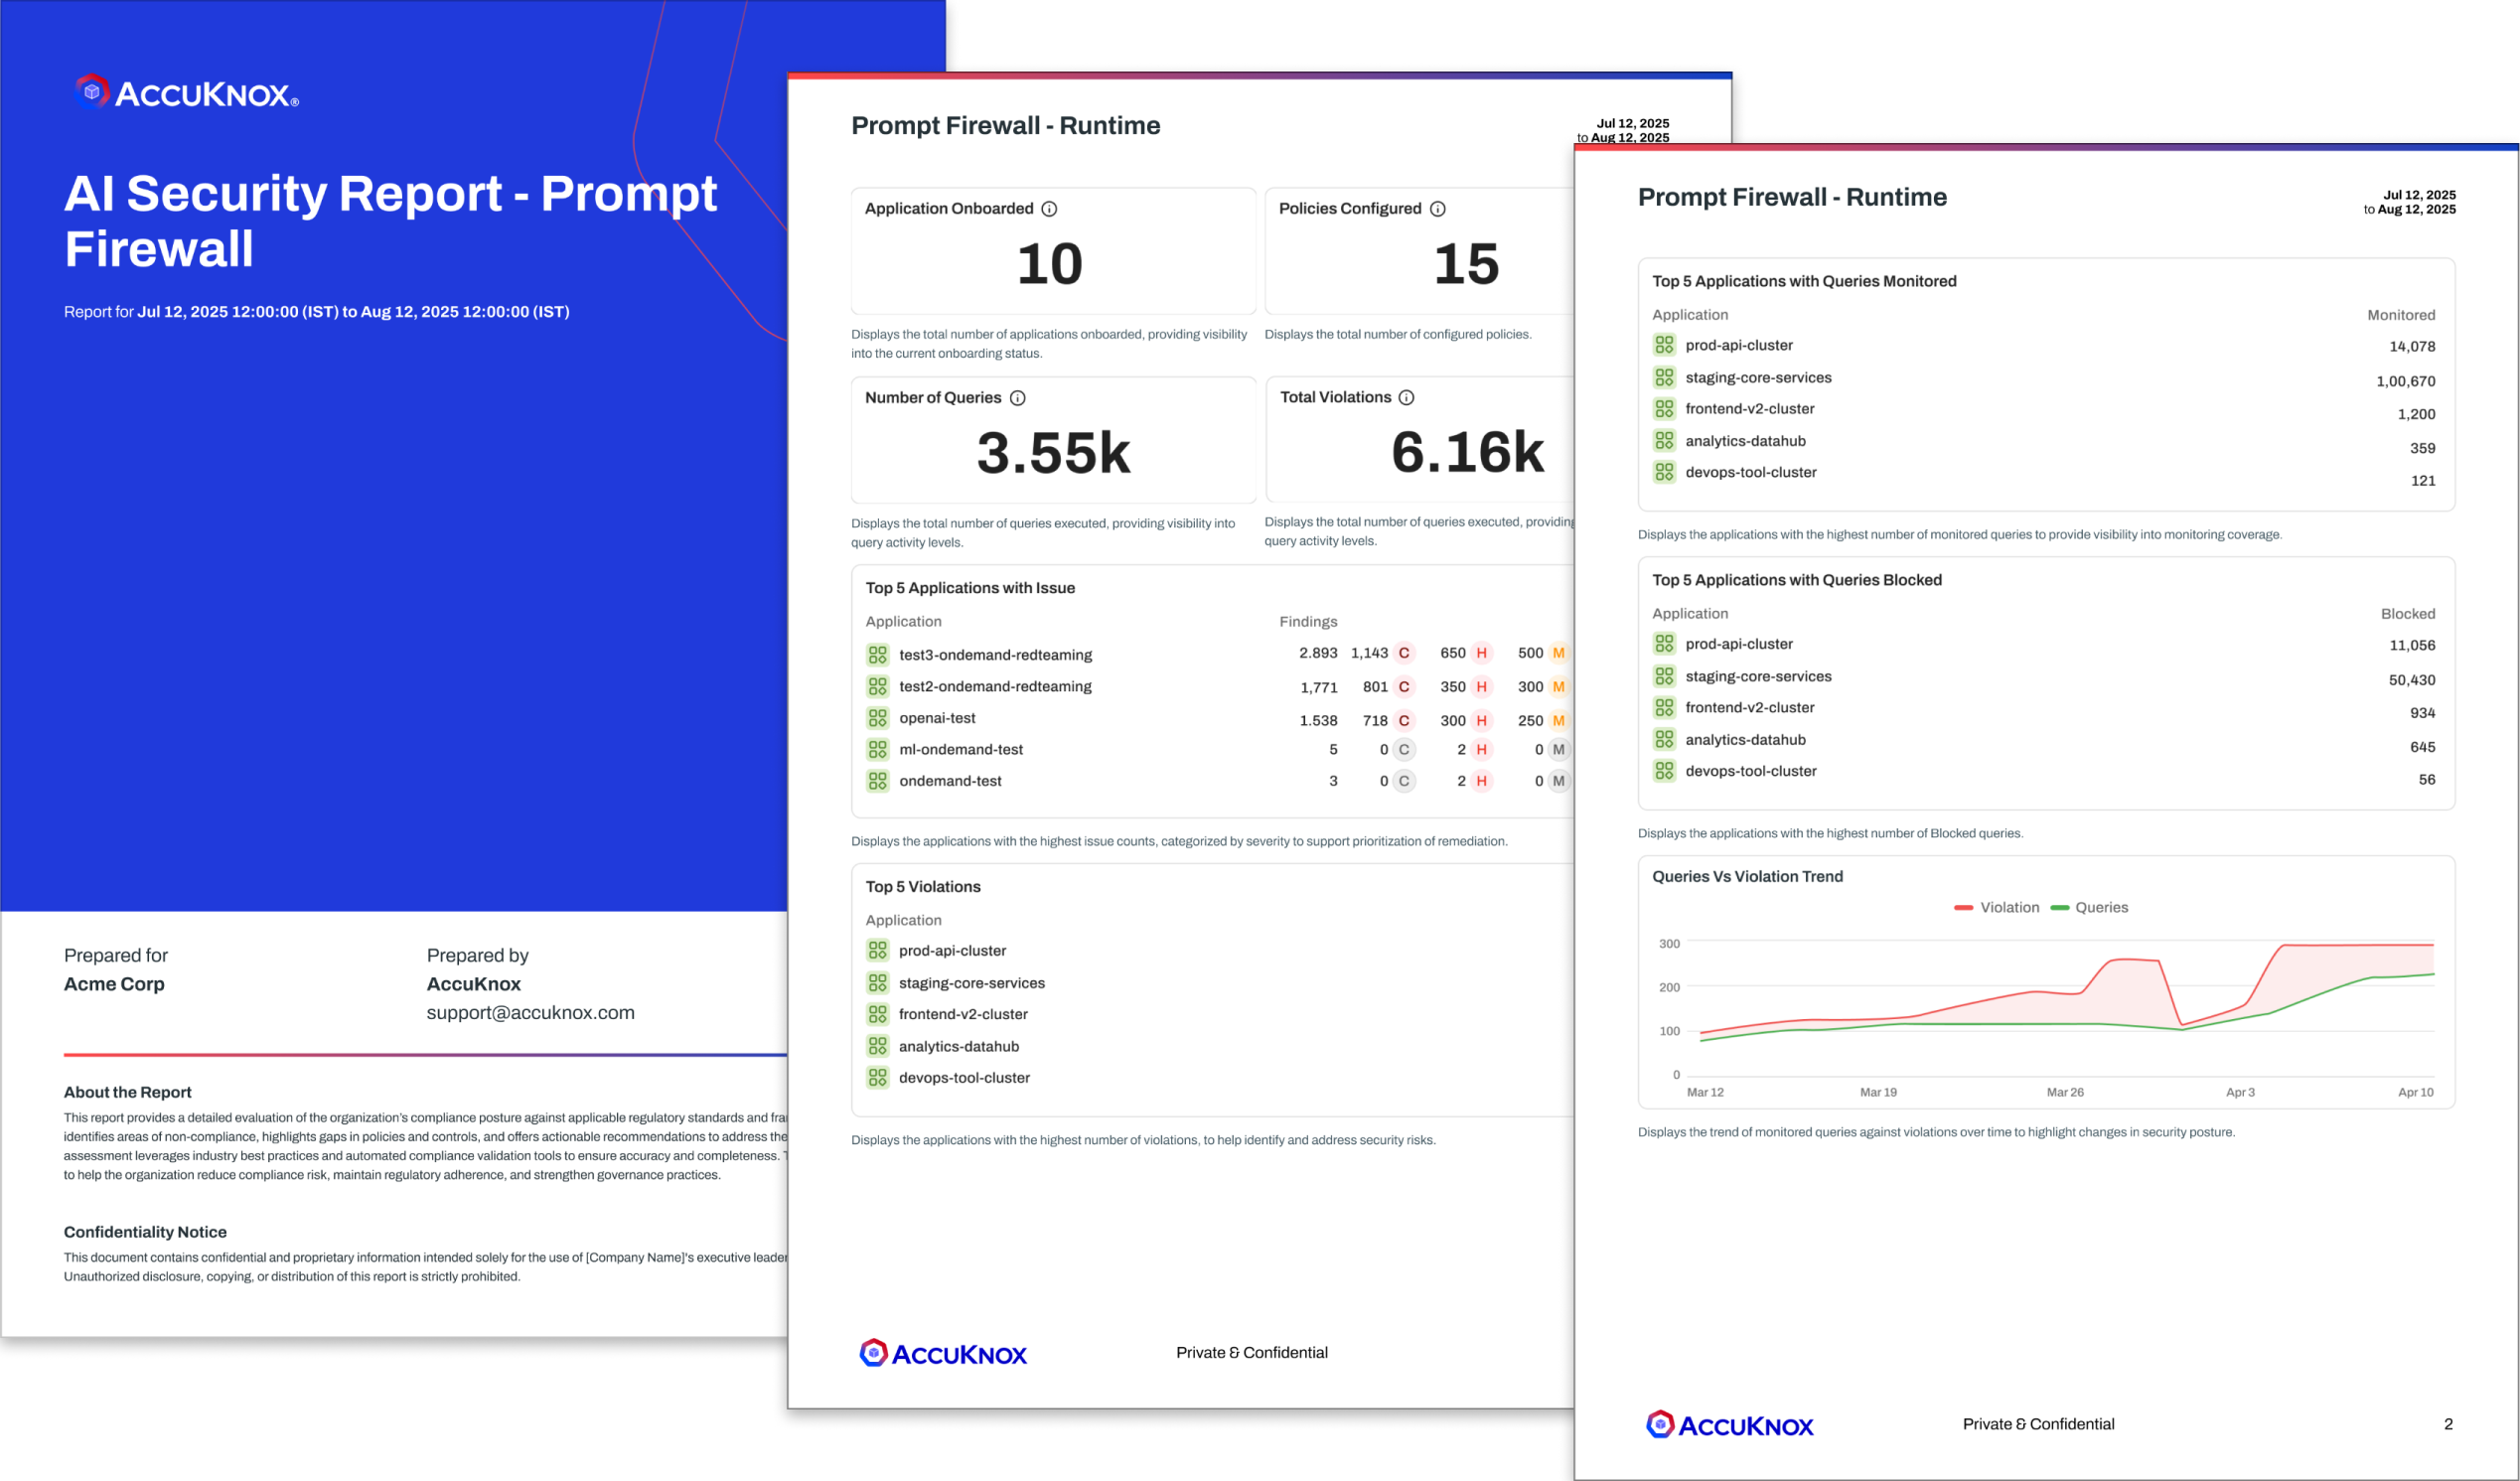
On-Demand Reports for AI Security
AI Security Key Differentiators

Runtime prompt firewall with LLM-as-judge sanitization and blocking
Automated AI red teaming for injections, hallucinations, toxicity, bias
Multi-layer AI security across models, agents, datasets, and pipelines
AI asset inventory with agent, model, and pipeline lineage mapping
AI detection and response for model misuse and infra misconfigurations

Detect and block AI-specific threats via model red-teaming, prompt filtering, dataset integrity checks, and secure ML supply-chain controls.
AI Security Competitive Stack Ranking




AI Security for AI/LLM Workload Security FAQs
Get a LIVE Tour
Ready For A Personalized Security Assessment?
“Choosing AccuKnox was driven by opensource KubeArmor’s novel use of eBPF and LSM technologies, delivering runtime security”

Golan Ben-Oni
Chief Information Officer
“At Prudent, we advocate for a comprehensive end-to-end methodology in application and cloud security. AccuKnox excelled in all areas in our in depth evaluation.”

Manoj Kern
CIO
“Tible is committed to delivering comprehensive security, compliance, and governance for all of its stakeholders.”

Merijn Boom
Managing Director
Trusted by Cybersecurity Leading Investors


Featured Customers




Awards & Recognitions


Investors




About Us
AccuKnox delivers a Zero Trust Security platform for AI, API, Application, Cloud, and Supply Chain Security. Incubated out of R&D innovator, SRI International (Stanford Research Institute), AccuKnox holds seminal Zero Trust security patents and is backed by top-tier investors including National Grid Partners, Dolby Family Ventures, Dreamit Ventures, Avanta Ventures, and the 5G Open Innovation Lab.